In fast-growing companies, employees often buy software faster than finance can track it. Someone needs a tool, puts it on their personal card, and then expenses it to the company later.
By the time the spend shows up on a monthly expense report, the subscription is already running and the money is long gone.
Finance is last to know about these purchases because the spend rides on a personal card, and a personal card only becomes visible once it's expensed. But there's a way to fix that.
By moving the buying onto a payment method finance controls, purchases become visible and capped the moment they happen, rather than weeks later. That shift, from control after the spend to control before it, makes a huge difference for finance teams struggling to reign in under-the-radar SaaS spending.
The spend finance can't see
Invisible SaaS spend is far more than a fringe problem. In Flexera's 2026 State of ITAM report, drawing on Deloitte's 2025 global ITAM survey, 69% of organisations said shadow IT and unauthorised SaaS purchases were rising as buying decentralised across teams, while only 36% had full visibility of their IT estate.
Alarmingly, this means that, for most companies, the majority of the software they depend on was bought somewhere finance can't see. And it's a trend that's only continuing in the wrong direction.
Why policy doesn't fix it
The obvious response is to tighten the rules, but the usual tools don't actually stop the purchase. An expense policy sets out what people should and shouldn't buy, yet nothing enforces it at the moment of spend, meaning it only bites once the claim is submitted. Spend reviews look at money that's already left, and reminders nudge behaviour without stopping a transaction.
Even a well-written policy then runs into a simple obstacle. When a team needs a tool to hit a deadline, the personal card is the quickest route, with no request form and no approval queue to wait on. Procurement is slower, so procurement loses. As long as expensing a personal card is the path of least resistance, you'll keep getting unwanted spend through this channel.
Move control to the point of purchase
The way around this is to make the controlled spending route as easy as possible. To do this, all you have to do is move control to the point of purchase rather than the point of reconciliation.
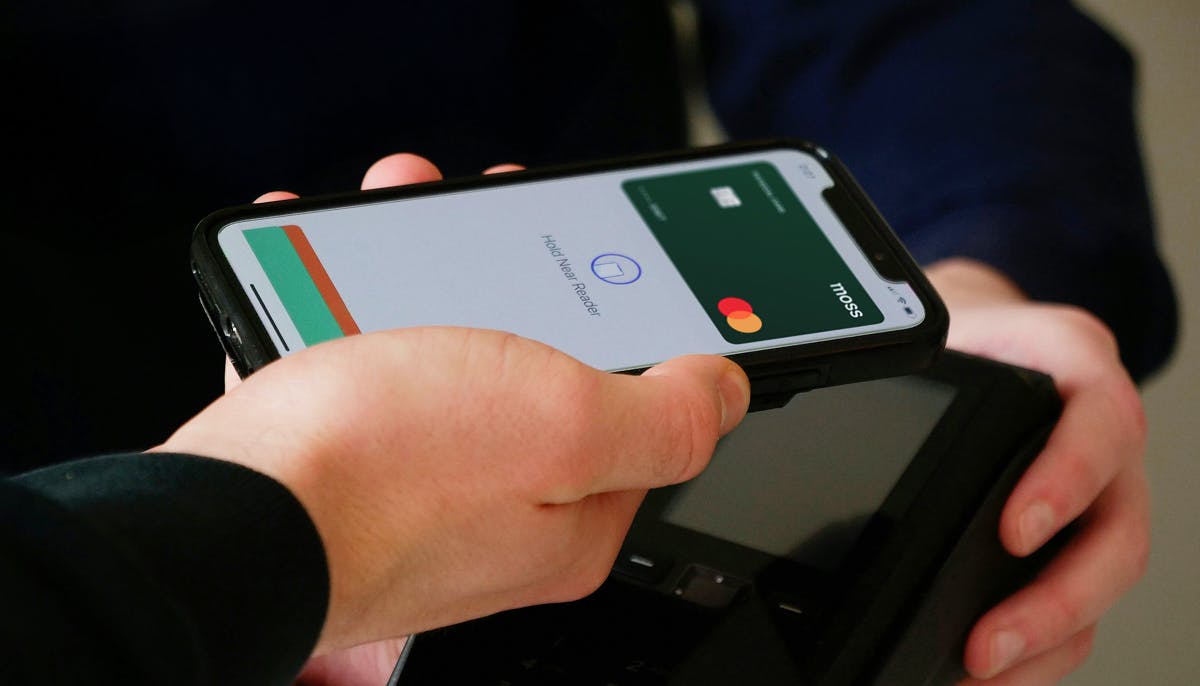
Company-issued virtual cards do exactly that by locking the card to a single vendor, capping it at a set limit, and issuing it only after a quick approval. Unsanctioned or over-budget purchases are declined as they're attempted, rather than discovered weeks later.
Because each card maps to one subscription, every tool becomes visible and individually freezable. Cancelling one when a tool is dropped or an employee leaves takes nothing else down with it.
Where Moss fits, alongside ITAM
Enabling smoother, more visible company spend is precisely the problem Moss was built to solve. It replaces personal-card expensing with virtual cards that carry merchant category rules, enforced limits and pre-spend approval, so control sits ahead of the purchase.
What it doesn't do is tell you how software gets used once it's bought, which licences are active, duplicated, or sitting idle. That's the job of an ITAM or SaaS-management tool. The two answer different questions. ITAM handles usage and adoption, while card controls handle the point of spend. Run together, shadow IT stops being invisible on both sides.
What changes at month-end
For a finance team, the difference shows up at month-end. The purchases that matter are visible, capped and reversible from the moment they're requested, and the quickest way for anyone to buy software becomes the route finance controls. Shadow IT doesn't vanish overnight, but the spend side of it stops being something you only find out about after the fact.
Find out more about Moss smart corporate cards here.